
Talview Biometric Information Privacy Policy
Last updated
1. PURPOSE AND SCOPE
Talview Inc. (Talview) uses biometric data only to confirm that the right person takes an exam and to protect the integrity of that exam. This policy states what biometric data Talview collects, why, who receives it, how long it is kept, and when it is permanently destroyed.
This policy applies to:
- every candidate who takes an exam proctored through Talview Proview or Talview Secure Browser
- every Talview employee, contractor and service provider who can access that data
Talview provides proctoring on behalf of its customers, the institutions and exam owners that run the exams. The customer decides which features are switched on for its exams. Talview processes biometric data only on the customer's documented instructions and under this policy. Where a customer contract sets a shorter retention period or stricter terms, the contract applies.
2. WHAT BIOMETRIC DATA TALVIEW COLLECTS
In this policy, biometric data means biometric identifiers and biometric information as defined by applicable law. That includes a scan of face geometry and any information derived from it that is used to identify a person. Which items below are captured depends on the features the customer enables for an exam.
| Data | When it is captured | What it is used for |
| Base photo (reference image of the candidate's face) | Pre-exam checks | The reference that later face images are compared against |
| Photo of the identity document | Pre-exam checks | Comparing the candidate's face with the photo on the ID |
| Face images during the exam | At intervals through the session | Confirming the same person is present throughout |
| Face match result | Each time a comparison runs | Recording whether the faces match. |
| Secondary camera and screen recordings, and the room scan | Through the session | Human review of exam integrity. These contain face images not used to create face templates |
| Video Recording from Primary Camera, Secondary Camera, Screen Recording | Through the session | Video is recorded for the examination. This is used for human review at the end of the examination for various flags that were generated. |
| Secondary Face Detection | Through the session | Secondary face means detecting and capturing any additional face showing up on the camera during the examination. |
What Talview does not collect: fingerprints, voiceprints, iris or retina scans, or hand geometry.
Talview does not use biometric data to infer emotion, age, gender, race or any other personal characteristic, and does not use it to identify anyone other than the candidate taking the exam. AI detection of a second person / secondary face in view flags that someone else is present; it does not identify who they are.
3. HOW BIOMETRIC DATA IS USED
Talview uses biometric data for two purposes only: verifying the candidate's identity, and protecting the integrity of the exam the candidate consented to take.
- No sale or profit: Talview does not sell, lease, trade or otherwise profit from biometric data.
- No advertising: Biometric data and other candidate data are never used for advertising, marketing or audience matching.
- No training without consent: Talview does not use a customer's biometric data to train or improve AI models without that customer's written consent.
- Mandatory Human in loop: Face match results and AI flags inform human reviewers. Talview does not qualify or disqualify a candidate on biometric data alone; the customer makes the final decision.
4. NOTICE AND CONSENT
No biometric data is captured until the candidate has read a written notice and given explicit consent.
- Notice: Before any capture, the candidate sees a notice stating that biometric data will be collected, the specific purpose, and how long it will be kept, with a link to the Talview candidate facing privacy policy - https://www.talview.com/en/privacy.
- Consent: The candidate must actively agree (a written release given electronically through “click-wrap” agreement) before the camera checks start. Talview records the consent text shown, its version and the time of consent.
- Declining: A candidate who declines is not captured. The customer arranges alternative methods for the candidate to appear for the examination.
- Minors: Where a candidate is under the age of consent in their jurisdiction, the customer obtains consent from a parent or guardian before the exam.
The customer can tailor the notice text for its candidates. Talview's consent screen meets the requirements of this policy, whatever text the customer adds.
5. HOW BIOMETRIC DATA FLOWS
Biometric data moves through six steps, and each step is encrypted and limited to the people and services named in section 6.
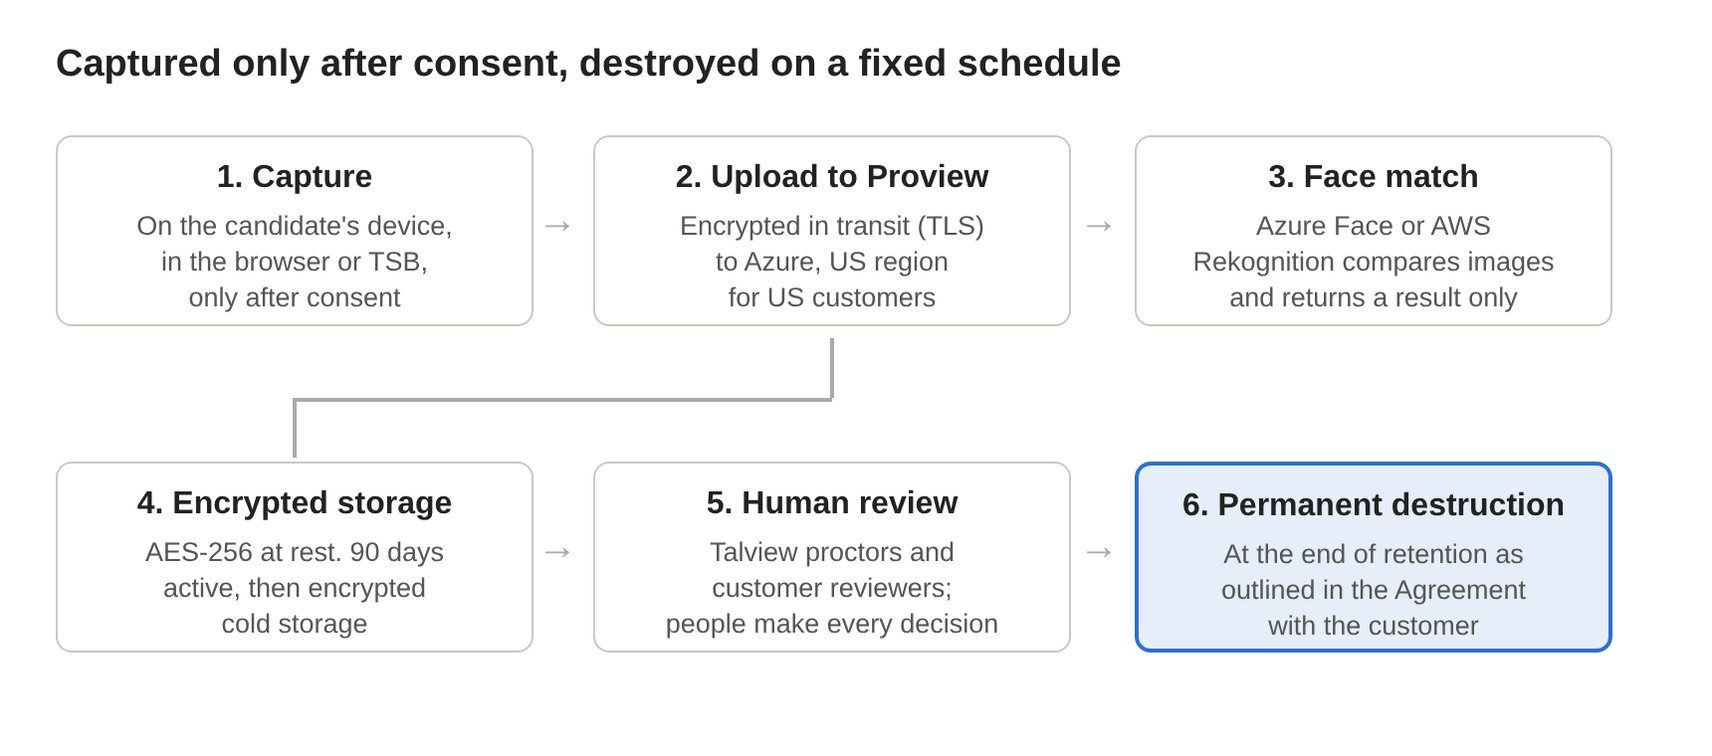
The face match service receives individual images and returns a match result; it keeps no copy. Everything else stays in Talview's encrypted storage in the customer's region until it is destroyed under section 7.
| Step | Stage | What happens |
| 1 | Capture | On the candidate's device, in the browser or TSB, only after consent. |
| 2 | Upload to Proview | Encrypted in transit (TLS) to Azure, US region for US customers. |
| 3 | Face matching | Azure Face or AWS Rekognition compares images and returns a result only. |
| 4 | Encrypted storage | AES-256 at rest. 90 days active, then encrypted cold storage. |
| 5 | Human review | Talview proctors and customer reviewers; people make every decision. |
| 6 | Permanent destruction | At the end of retention as outlined in the Agreement with the customer. |
The face match service receives individual images and returns a match result; it keeps no copy. Everything else stays in Talview's encrypted storage in the customer's region until it is destroyed under section 7.
6. WHO RECEIVES BIOMETRIC DATA
Talview discloses biometric data only to the customer that runs the exam, to the service providers listed below under written contract, with the candidate's consent, or when required by law or a valid legal order.
| Provider | Role | What it receives | Kept by the provider |
| Microsoft Azure | Hosting and encrypted storage. US regions for US customers | All session data | Under Talview's schedule in section 7 |
| Microsoft Azure Face API | Face matching | Individual images, per comparison | Not kept after the match |
| AWS Rekognition | Face matching | Individual images, per comparison | Not kept after the match |
| Persona | ID document verification, where the customer enables it | ID image and face image | Not kept after the match |
| Talview proctors, including affiliate AIWF Technologies Pvt Ltd | Human review of sessions | View-only access through the Talview platform | No copies kept, reviewing only through Talview’ Proview Interface. |
Every provider is bound by contract to use the data only to deliver its part of the service, to protect it to at least this policy's standard, and to delete it on Talview's instruction. The contractual and privacy obligations are passed through to the downstream vendors and periodically reviewed.
7. RETENTION AND DESTRUCTION SCHEDULE
Talview permanently destroys biometric data at the earliest of two points:
- when the purpose is fulfilled, meaning the session review and any review or appeal period set in the customer contract has closed
- when the customer instructs deletion outlining in the agreement, or its contract ends
| Data | Active storage | Then | Destroyed no later than |
| Face images, ID photo and session recordings | 90 days from session completion | Moved to encrypted cold storage | End of the customer retention period as outlined in the agreement or termination of the agreement |
| Base photo | Kept to verify the same candidate in later sessions for the same customer | Stays in active storage | End of the customer retention period as outlined in the agreement or termination of the agreement |
| Face match result | Stored with the session | Follows the session | With the session data |
| Copies at face matching providers | Not kept | None | Immediately after the match |
| Backups | Rolling 30-day backups | Overwritten | Within 30 days of deletion from primary storage |
How data is destroyed. Deletion is permanent and irreversible, run by automated storage lifecycle rules. When a contract ends, Talview confirms deletion to the customer in writing on request.
Legal holds. Deletion is paused only where a law, court order or active investigation requires it. Each hold is recorded with its reason, and the data is destroyed once the hold is lifted.
Early deletion. Customers can ask for deletion at any time. Candidates can ask through the customer or at privacy@talview.com.
8. SECURITY
Talview protects biometric data to at least the standard it uses for its most sensitive confidential information.
- Encrypted in transit (TLS) and at rest (AES-256)
- Access limited to named roles that need it, through the Talview platform only
- Every access to media files is logged
- Controls audited under SOC 2 Type II and ISO 27001
- Customers notified of any security incident affecting their data without undue delay, as set out in the Data Processing Agreement
9. REQUESTS FROM CANDIDATES AND CUSTOMERS
Candidates can ask to see or delete their biometric data. Requests go to the customer that ran the exam or to privacy@talview.com; Talview works with the customer to answer within the time the law and the Data Processing Agreement require.
10. APPLICABLE LAWS
Talview platform practices are in compliance with the requirements of GDPR, CCPA, PIPEDA, LGPD, PDPA, DPDP Act. In the event there are some geographical laws stricter than the ones mentioned here, Talview platform is configurable to the stricter requirements for protection of candidate data, including their biometric data.
11. REVIEW AND CONTACT
Legal and the Data Protection Officer review this policy every year, and whenever Talview changes how it collects or uses biometric data.
Questions: privacy@talview.com